
Claude Code secrets are leaking onto GitHub, and the scary part is how it happens: one click that feels completely safe. Researchers just counted about 2,500 real credentials sitting in public repositories. If you’ve ever used Claude Code, here’s how to check yourself and clean up in about 20 minutes.
The one click that leaks your Claude Code secrets
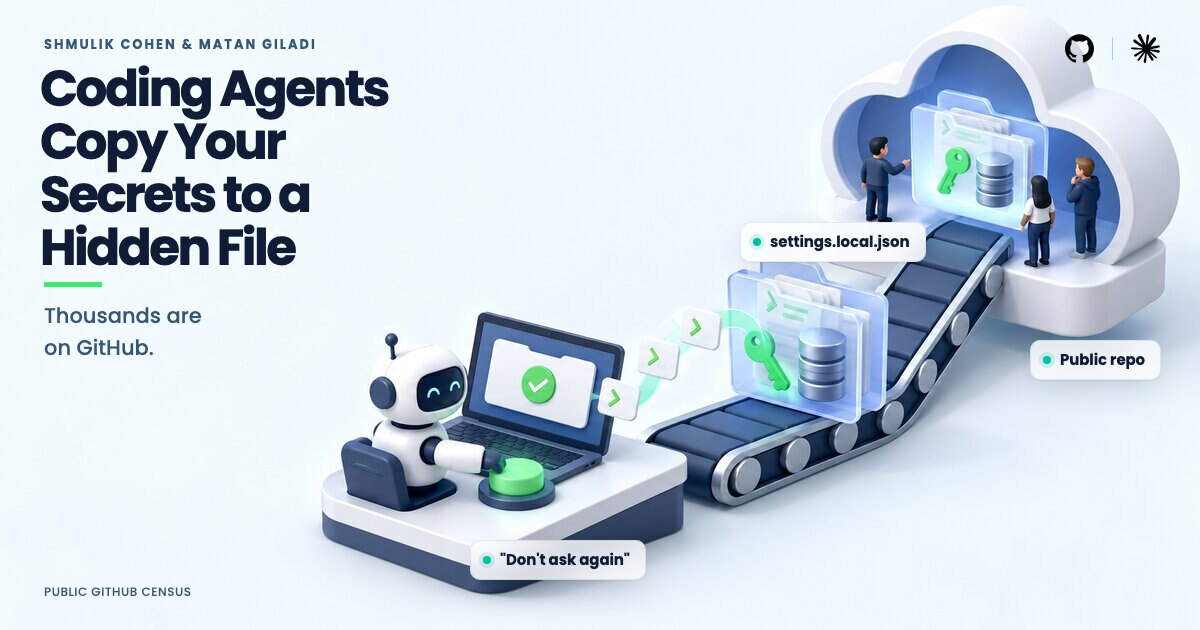
When Claude Code wants to run a shell command, it asks permission. You’ve seen the prompt. There’s a button that says “Yes, and don’t ask again,” and clicking it feels responsible. Fewer interruptions, faster workflow, what could go wrong?
Here’s what. That approval gets saved as a rule in a file called .claude/settings.local.json on your machine. And the rule isn’t just the command pattern. It’s often the entire command, word for word, exactly as it ran.
Say you asked Claude Code to connect to your database and the command was psql -U admin -W mydb followed by your password in plain text. That password, all of it, now lives in a settings file. Unencrypted. Sitting in your project folder. Waiting for the next git add .
The approval log doesn’t care that the password was never meant to leave your laptop. It just records what happened.
How 2,500 credentials ended up in public repos
Security researchers at Apiiro scanned GitHub and found more than 104,000 copies of that settings file in public repositories. Most were harmless. But 1,122 of them, from 63 different organizations, contained real Claude Code secrets.
Digging through git history and related files, they counted 2,539 distinct credentials across nearly 2,000 repositories. The haul included database passwords, cloud service keys, SSH logins, and GitHub tokens. Some affected repos belonged to software companies and service providers, places you’d assume knew better.
This isn’t a Claude-only disease, by the way. Researchers found that other coding agents don’t save full commands by default, but GitGuardian’s earlier research showed Claude Code-assisted commits leak secrets at roughly double the normal rate, 3.2% versus a 1.5% baseline. Claude Code secrets spread twice as fast, in other words. Speed has a price, and it’s usually a credential.
Ars Technica has the full story on the research here, and Apiiro’s original writeup with methodology lives on their blog.
Why deleting the file doesn’t fix it
Intuition says: find the file, delete it, push, done. Wrong.
Git remembers everything. Even after you remove the file, the secrets stay in your repository’s history, recoverable by anyone who knows where to look. Forks make it worse. If anyone cloned or forked your project while the file was public, deleting your copy does nothing to theirs.
There’s also a quieter trap. Claude Code adds the file to your global gitignore list, which sounds protective. But that ignore rule only exists on the machine where you clicked the button. Clone the project on a second laptop, or a teammate pulls the repo, and the ignore rule never traveled with it. The file gets committed anyway, sometimes by Claude itself during an unrelated task.
Standard secret scanners miss these leaks too, because the passwords hide inside command strings instead of sitting in the usual .env patterns they’re trained to flag. It’s a genuinely awkward failure mode. We saw the same “tool quietly uploads your git history” pattern with ZCode last month, so this is the second time this year Claude Code secrets (or their cousins) went walkabout.
Check if your Claude Code secrets are exposed in two minutes
Don’t panic yet. Check first. Open a terminal in any project where you’ve used Claude Code and run:
# does the risky file exist in the project?
find . -name "settings.local.json" -path "*/.claude/*"

# has it EVER been committed, including old history?
git log --all --oneline -- .claude/settings.local.json

# peek at what's actually inside right now
cat .claude/settings.local.json
That second command is the important one. No output means the file never entered git history and you’re clean on this repo. Output means it was committed at least once, and the commits listed are your exposure window.
Then look at the file itself. Search for anything sensitive inside approved commands: passwords after -p flags, tokens in URLs, connection strings, API keys. If the file only contains harmless patterns like Bash(npm run build), breathe easy.
For public repos, do one more pass on GitHub itself. Search your repo for settings.local.json, and check the Insights view for forks. Private repos are safer, though the same file becomes a landmine the day you ever open-source the project.
The 20-minute cleanup, step by step
Found something? Here’s the order that actually works. Total time, about 20 minutes for a typical repo.
- Rotate the exposed credentials first. This beats everything else, because your keys are already public the moment they hit history. Change the database password, reissue the AWS keys, regenerate the GitHub token. Rotation makes the leak historical instead of dangerous.
- Stop tracking the file. Run
git rm --cached .claude/settings.local.json. The--cachedflag keeps your local copy (Claude Code still needs it) while removing it from git. - Add the ignore rule to the project’s .gitignore, not just your global one. The command is
echo ".claude/settings.local.json" >> .gitignore. This protects every clone, every teammate, every future machine. It’s the step Anthropic’s default only does for your original laptop. - Commit the removal and push.
- Scrub the git history. This is the part most guides hand-wave, and skipping it leaves the old secrets recoverable. The commands are in the next section.
- Verify the repo is clean with a scanner. Run
gitleaks detect --source . --verbose, or enable GitHub’s built-in secret scanning in the repo settings. It’s free on public repos and catches future leaks automatically.
Step 5 is the one people skip
Force-pushing rewritten history sounds scary, so people skip it. Understandable. But understand the trade: without the scrub, anyone with the repo URL can still pull the old commits and read yesterday’s password. Since you already rotated in step 1, the old commits hold dead credentials, which lowers the urgency. Still, scrub when you can, and warn collaborators before you force-push so nobody loses work.
# using git-filter-repo (pip install git-filter-repo)
git filter-repo --path .claude/settings.local.json --invert-paths
git push origin --force --all
git push origin --force --tags
One more loose end: forks. If your repo is public and someone forked it before the cleanup, your scrub doesn’t reach their copy. GitHub support can help with takedowns for sensitive data, and rotated keys make the forks toothless. This is exactly why step 1 came first.
Using Claude Code without the leak risk
You don’t need to stop using Claude Code. You need three habits.
First, never type credentials directly into commands you’ll approve with “don’t ask again.” Set environment variables instead, or use a secret manager, so the sensitive values never enter the command text. If a command needs your password, let it prompt you rather than embedding it.
Second, add .claude/settings.local.json to the project .gitignore of every repo where you use Claude Code, today, before any incident. Thirty seconds of chore now beats an hour of forensics later.
Third, run a leak scan monthly. Gitleaks takes minutes, and a recurring pass keeps Claude Code secrets from piling up unnoticed in repos you forgot about. The vibe coding security checklist covers the rest of the pre-ship hygiene worth building. The uncomfortable pattern across all of this, from the Pentagon agent leak to this one, is that AI tools move fast and quietly, while our security habits stay slow. Closing that gap is the whole game.
Your next move
Run the three check commands on your main project right now. Two minutes. If the file never touched git, add it to .gitignore tonight and you’re done forever. If it did, start the rotation, because that clock is the only one that matters. The full Apiiro methodology is worth a read if you want to see how researchers caught it.
Paste your password into a chat once and it’s a story. Paste it into an approval button and it’s a leak with a public URL. Check today, fix in 20 minutes, and keep building.